Mac security, built for the Mac.
CrowdStrike and Microsoft Defender protect a Windows estate well, and if you run one, you probably have them. The real question is what your Macs get inside a cross-platform model. We secure Apple with security built for Apple: deep, native, and light enough to stay out of your people’s way.
Strong tools. Built for someone else’s fleet.
CrowdStrike and Microsoft Defender are excellent cross-platform EDR, with world-class threat intelligence and hunting. We are not here to say otherwise, and if your business is Windows-first, they earn their place.
But both were built to secure Windows first, and they bring the Mac along inside that model. They detect and respond well. What they don’t do is manage and harden the Mac itself: new macOS support lands on their schedule, compliance baselines and configuration were never their job, and on Apple silicon they lean on a management platform like Jamf just to deploy cleanly. On the Mac, that gap is where risk lives.
Apple-native. Not Apple-added.
Jamf Protect is built only for Apple, on Apple’s own security frameworks. That single fact changes what your Macs actually get.
The Mac is one more OS
New macOS support lands when the vendor gets to it. It detects and responds, but it doesn’t harden or configure the Mac, and it needs a separate MDM to deploy and to act. Compliance baselines aren’t part of the deal.
The Mac comes first
Built on Apple’s Endpoint Security framework, so new macOS, iOS and visionOS are supported from day one. A light, Apple-framework agent with on-device detection, the management to act on what it finds, and compliance mapped natively to Apple.
The whole picture. Endpoint and network.
Endpoint protection
Next-gen antivirus quarantines known malware and its variants, hardens Macs against fileless and Living-off-the-Land attacks, and controls removable storage, all with minimal impact on the machine.
Threat detection & response
On-device behavioural analytics mapped to MITRE ATT&CK, powered by Jamf Threat Labs intelligence, with remediation through the same platform that manages the Mac. Threats get fixed, not just flagged.
Web & network defence, ZTNA
Jamf Security Cloud blocks phishing, malicious domains, command-and-control traffic and cryptojacking, filters content, and gives Zero Trust access on any network, with no VPN to wrestle.
Compliance & visibility
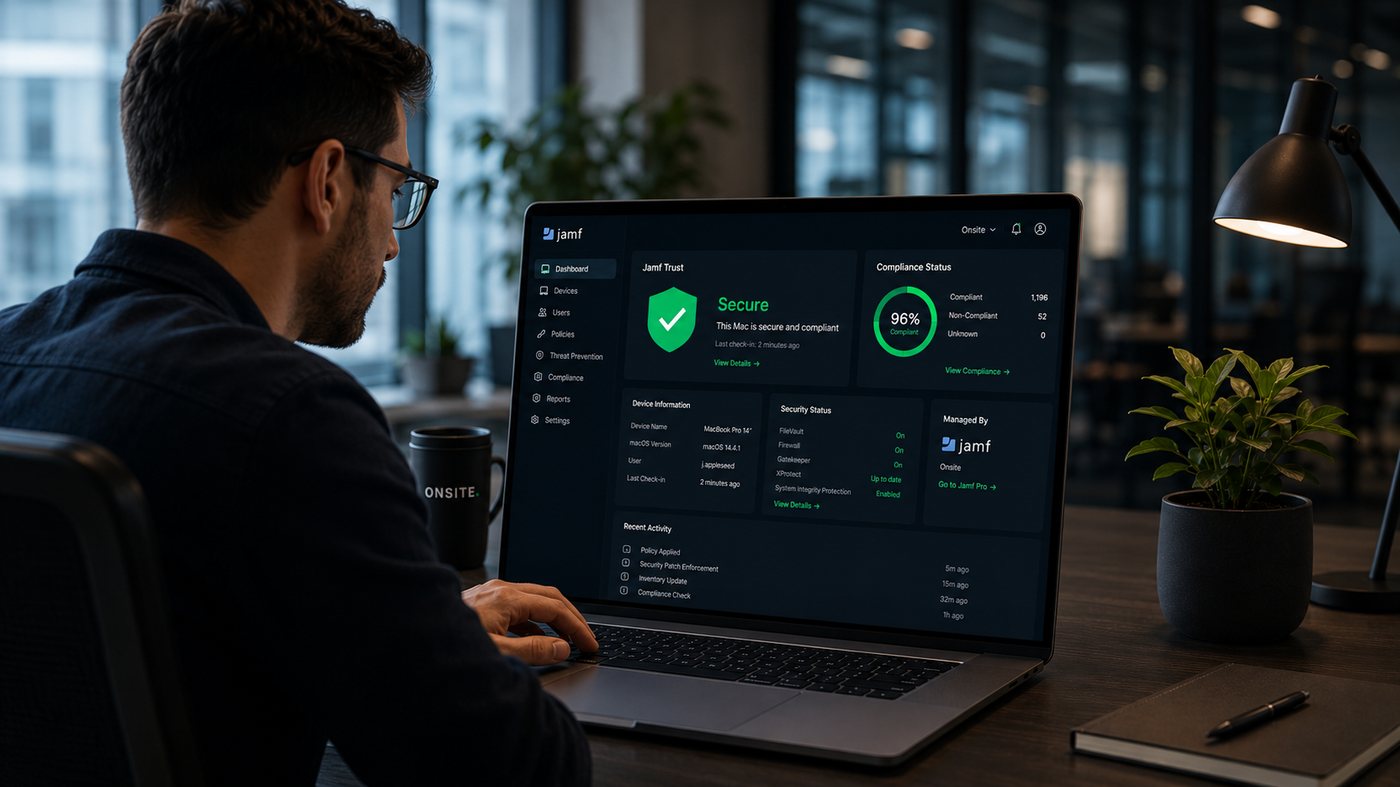
Continuous CIS, NIST 800-53, NIST 800-171 and DISA STIG baselines, CVE and vulnerability reporting, risk scoring for zero-trust decisions, and rich Mac telemetry streamed to your SIEM.
What’s next for Mac security.
Apple-native data loss prevention
Finds sensitive data on the Mac and stops it reaching unapproved destinations, using controls built into macOS.
Release: Targeted Q4 2026
AI governance
See, control and prove the AI tools running on your Macs, on the security platform you already run.
Release: Available now
Explore AI governance →Where Apple-built pulls ahead.
Day one on every new OS
A new macOS ships and Jamf Protect supports it that day. Cross-platform agents add it when they reach it.
A light, Apple-framework agent
Built on Apple’s own frameworks and tuned for Apple silicon, so it stays out of your people’s way.
Detect and fix on one platform
Because we secure and manage the Mac together, a detection becomes a remediation, not another ticket.
Compliance you can prove
Mac hardening mapped and reported against CIS, NIST and STIG, not approximated by a Windows-shaped baseline.
Apple-specific intelligence
Jamf Threat Labs hunts Mac and mobile threats specifically, so detections reflect how Apple is actually attacked.
Privacy kept intact
Security that works with Apple’s privacy model, not around it, so people stay protected without feeling watched.
Run us alongside. See the difference.
This isn’t rip-and-replace. If your team has standardised on CrowdStrike or Defender across Windows, keep it. In fact, on Mac those tools already lean on a management platform like Jamf to deploy and to act, so we’re in the picture either way. Run Jamf Protect alongside and the gap shows itself.
Side by side, Jamf Protect surfaces what a cross-platform agent leaves on the table: Mac compliance drift against CIS, NIST and STIG, day-one coverage when a new macOS ships, content filtering and Zero Trust access, and richer Apple telemetry streamed straight into your SIEM or XDR, including Microsoft Sentinel, Splunk and Google SecOps. Keep your EDR. Add the Apple depth, the compliance and the management that make it actually land on the Mac.
Security that lets people work from anywhere.
 Zero-touchsecured at first lid-open
The Up & Up Group onboards new Macs with zero-touch enrolment, so every device is hardened, compliant and protected the moment its lid first opens, before it reaches the person using it.
Watch the story →The team that’s all-in on Apple.

A Jamf Elite Partner, securing Apple estates across Africa. We deploy Jamf Protect, tune the analytics to your environment, map your compliance baselines, and respond when something moves. Security is only as good as the team running it.
See what your Macs aren’t telling you.
Book a security review. We’ll show you where your Apple estate is exposed today, what your current tools can and can’t see on the Mac, and the most practical way to close the gap.